Single sign-on and provisioning
Microsoft Entra ID, Azure AD, ADFS and SAML 2.0 for staff. Role-based permissions down to facility and function level. Resident accounts are separate from staff identity by design.
Trust Center
This page states what OptimoGov holds, where your data lives, how the resident portal handles accessibility, and what we have not certified. The last part matters as much as the first. Ask every vendor you evaluate for the same disclosure.
Last reviewed September 2026. Security contact: security@optimogov.com
Certifications and attestations
Several vendors in this category publish a security page that names no certification at all. Others hold a strong authorization and bury it in a blog post. Below is the full ledger, including the gaps.
Some vendors present Microsoft Azure's certifications as their own. We separate them. Where a control is inherited from Azure we say so, and where it is our own audited scope we say that instead.
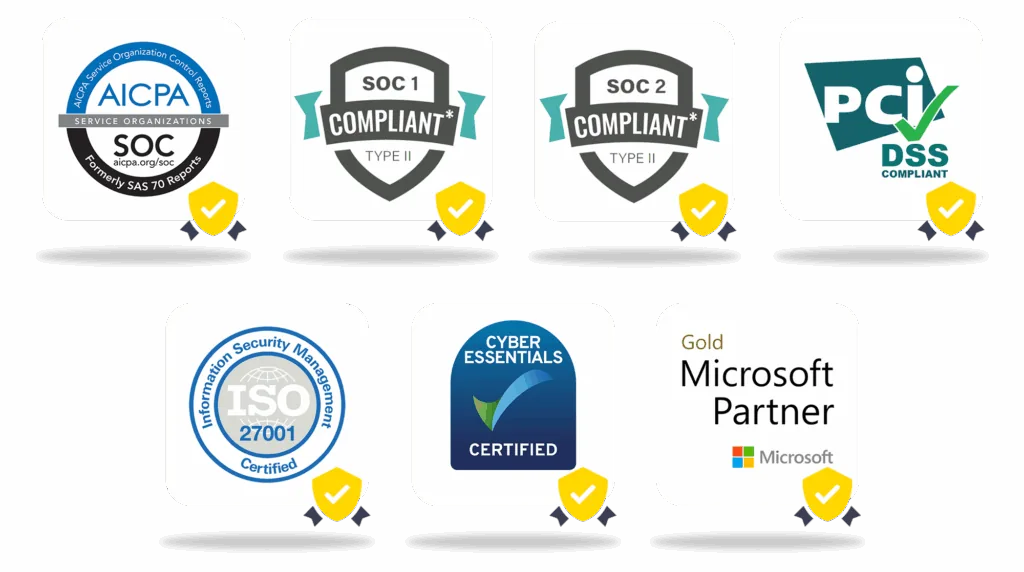
Information security management system certification covering the OptimoGov platform and its operating organization. Certificate and scope statement supplied in the security pack.
Independent examination of security, availability and confidentiality controls over a defined observation period. Report released under NDA on request.
Controls relevant to financial reporting, which your auditor may request given the platform handles receipting and revenue.
Card data is handled by the gateway, not stored in OptimoGov. Attestation of compliance and the scope of our cardholder data environment are in the security pack.
Independent testing four times a year against the platform and the resident portal, with remediation tracked to closure. Executive summary available on request.
A United Kingdom government scheme. We list it for completeness and note that it carries no recognition in United States or Canadian procurement.
We are not currently on the GovRAMP authorized product list in any status. Where your state requires GovRAMP or a state equivalent such as TX-RAMP, tell us during the RFP and we will confirm our position on the required timeline rather than let you find out at contract.
Not held and not on our roadmap. OptimoGov is sold to state, local and municipal government, not to federal agencies.
We do not hold a Sourcewell, OMNIA Partners, NASPO ValuePoint, BuyBoard or TIPS contract at present. Where your policy allows it, we can support a piggyback off an existing award, a state term contract or a sole source justification. See procurement paths.
Data residency and privacy
Region is selected at contract and does not change without your written instruction. For Canadian agencies this is a legal requirement rather than a preference, and we treat it that way.
| Item | United States | Canada |
|---|---|---|
| Primary hosting | Microsoft Azure, US region | Microsoft Azure, Canadian region |
| Backup location | Azure Backup Vault, same country | Azure Backup Vault, same country |
| Encryption | TLS in transit, encrypted at rest | TLS in transit, encrypted at rest |
| Applicable privacy regimes | State privacy laws including CCPA and CPRA, COPPA for participants under 13, FERPA where school data is involved | PIPEDA, provincial privacy legislation, Quebec Law 25 |
| Language of service | English | English, with French for Quebec deployments |
| Data processing agreement | Available for signature | Available for signature |
| Subprocessor list | Published and versioned | Published and versioned |
| Data export on exit | Full structured export in machine-readable format | Full structured export in machine-readable format |
Quebec deployments: OptimoGov supports French-language resident-facing content and GST, HST and QST handling. Confirm the current scope of French coverage with us before issuing a solicitation that requires it.
Accessibility
The Department of Justice rule under ADA Title II requires state and local government web content and mobile applications to meet WCAG 2.1 Level AA. A resident reservation and registration portal is in scope. So is the confirmation email, the invoice and the mobile view.
Compliance dateApril 26, 2027
Public entities serving a population of 50,000 or more.
Compliance dateApril 26, 2028
Public entities under 50,000, and every special district government regardless of size. Independent park and recreation districts fall here.
Dates reflect the compliance extension published in April 2026. The WCAG 2.1 AA standard itself did not change.
Platform security
Microsoft Entra ID, Azure AD, ADFS and SAML 2.0 for staff. Role-based permissions down to facility and function level. Resident accounts are separate from staff identity by design.
99.9% availability contracted. Disaster recovery plan with defined recovery point and recovery time objectives, stated in your agreement rather than left general.
Who changed a permit, a rate, a refund or a deposit deduction, when, and what the value was before. Retained and exportable, which is what a records request or an internal audit needs.
Card data is tokenized at the gateway. OptimoGov does not store primary account numbers. Reduces your PCI scope rather than extending it.
Quarterly independent penetration testing, secure development policy, dependency and vulnerability monitoring, and remediation tracked to closure.
A published route for researchers and for your own security team to report an issue, with acknowledgement and remediation commitments. Report a vulnerability
Documentation
One request returns everything your security questionnaire, your attorney and your purchasing officer need. Reports issued under NDA are marked below.
We would rather your IT reviewer clear us in week one than raise a blocker in week nine. Send the questionnaire and we will return it completed.